Showing posts with label Network & Security Virtualization. Show all posts
,

NSX-T | Security

Hi Guys,

I hope that you all are doing well with your beloved ones. Stay Home, Stay Safe, Keep Learning and Keep Growing.

So, In my older posts, I wrote about basic routing setup and a bit about DFW from Policy interface but today I thought to cover-up the same thing from Advance interface with some additional features.

So, let's discuss about below points-

- Distributed Firewall
- Edge Firewall
- Bridge Firewall (This is not available in policy interface) 

Because I will have to cover bridge firewall that's why including below in this post
- ESXi bridge cluster
- L2 bridging

I am sorry but no theory!! VMware has already done a great job on their website. Replicating same text is not a wise thing but yes, here is the excellent notes from VMware Documentation about the same

In this post, I will try to share all practical work. From where exactly in NSX-T, you can apply all these firewall rules from advance interface.

I have created a video, so, go ahead and play below video. Do remember to comment on blog to share how did you find it.

Distributed Firewall - So, it is distributed across the platform and applicable on entire infrastructure but we can decide where we want to apply it either on DFW leve, on Portgroups, on VM etc..Hope there is no doubt but if any then feel free to comment please. Ok, so hit the play button now.


Edge Firewall - Just play below video guys


Bridge Firewall-

This firewall basically is to restrict the traffic between VLAN and vxlan. If you know the L2 bridge  in NSX-V then it would be easier to understand and if you don't know then please read out here

Creating video on this is not feasible for me as of now because I don't have like setup. If I will have any such setup then will surely create one and will share with you guys!!


Thank you,
vCloudNotes

NSX-T | Policy or Advance Interfaces

Hi Guys,

While working on NSX-T, I noticed that the component (Like Tier-0, Tier-1, or any logical switch) which I created using the below interface (Advance Networking & Security) doesn't come up in the "Networking" tab.

Advance Interface


Policy Interface
But the component which I created in the "Networking" tab that does show in the "Advance Networking & Security" tab with an icon ⊜ which means that it is protected object and in read-only mode and cannot be configured through "Advance Networking & Security" tab.

After a little bit of study, I found that both interfaces do the same work. Just difference is that

- If you are deploying a new environment with NSX-T 2.4 or later then to use this policy based interface is the best to proceed.
- Some features (Below is the detail) are not available in the policy-based interface so to use those feature you can use Advance interface
- If you are upgrading to NSX-T 2.4 or later, continue to use Advance Networking & Security interface.

Below is the detail of when to use policy-based and when to use advance interface for any configuration in NSX-T


Policy Interface Advanced Interface
Most new deployments should use the policy-based interface. Deployments which were created using the advanced interface, for example, upgrades from versions before the the policy-based interface was present.
NSX Cloud deployments Deployments that integrate with other plugins. For example, NSX Container Plug-in, Openstack, and other clouds management platforms.
Networking features available in the Policy interface Networking features available in the Advanced interface
DNS Services and DNS Zones Layer 3 forwarding for IPv4 and IPv6
VPN Forwarding up timer
Forwarding policies for NSX Cloud Change internal transit network IP

VIP HA support on Tier-0

Standby relocation

Route advertisement filtering based on the list of prefixes on Tier-1

Loopback creation

BGP multihop

BGP source addresses

Static routes with BFD and interface as next-hop

Metadata proxy

DHCP server attached to an isolated segment and static binding
Security features available in the Policy interface only Security features available in the Advanced interface only
Endpoint Protection Ability to enable or disable Distributed Firewall, Identity Firewall, and Gateway Firewall
Network Introspection (East-West Service Insertion) Distributed Firewall session timers
Context Profiles - L7 applications, FQDN Exclusion lists
New Distributed Firewall and Gateway Firewall Layout - Categories, Auto service rules CPU and memory thresholds

Sections for stateless rules

Bridge Firewall

Section Locking

Distributed Firewall rule IDs

Distributed Firewall rules based on IPs in source and destination

Note that if you are using the "Advanced Networking & Security" interface then us it only and if you are using "Policy Interface" then use only that interface. Do not use both interfaces to create objects. However, objects which you create in "Policy Interface" can be visible in "Advance Networking & Security" but vice-versa doesn't happen.

Now, there is a difference in names as well. Refer to the below table, please and remember both do the same thing just name is different due to interface difference.


Objects Created Using the Policy Interface Objects Created Using the Advanced Interface
Segment Logical switch
Tier-1 gateway Tier-1 logical router
Tier-0 gateway Tier-0 logical router
Group NSGroup, IP Sets, MAC Sets
Security Policy Firewall section
Rule Firewall rule
Gateway firewall Edge firewall


All this I learned from https://docs.vmware.com/en/VMware-NSX-T-Data-Center/2.4/nsxt_24_admin.pdf from page number 12.

Hope you find this information informative. Stay tuned for more information.


Thank you,
vCloudNotes


, ,

NSX-T | Getting Started with PowerCLI

Hi Guys,

I am working on PowerCLI for NSX-T and trying to do all the operations as we could do in NSX-V. it is bit different yet simple so I thought to share what I have learned so far. below is a glimpse of the same. 

Also, there is a good article from VMware for the beginners to understand the same. I too learned from here but I was able to do more operations by understanding the given basics in the above link.

Explore it and let me know if you need any assistance with it. 

To connect NSX-T manager in PowerShell

#Connect-NsxtServer -server FQDN\IP


To get NSX-T manager details
function nsxnode{$nodesvc = Get-NsxtService com.vmware.nsx.node
$nodesvc.get()


To get the transport zone name and its relevant id
$tzone = Get-NsxtService com.vmware.nsx.transport_zones
(($tzone.list()).results) | Select display_name, ID


To get the name of all logical switch's name

 $tls = Get-NsxtService com.vmware.nsx.logical_switches
(($tls.list()).results).display_name


To get the name of all logical routers' name
$Tier1 = Get-NsxtService -Name com.vmware.nsx.logical_routers
($Tier1.list()).results.display_name


To create Tier-1 or Tier-0 router
$rname = Read-Host "Tell me the Tier-1 router name to set"
$tier1 = Get-NsxtService -Name com.vmware.nsx.logical_routers
$createt1 = $tier1.Help.create.logical_router.Create()
$createt1.display_name = $rname
$createt1.router_type = "TIER1" #Change it to TIER0 if you want to create Tier0 router
$tier1.create($create1)


To create logical switch
$segments = Get-NsxtService com.vmware.nsx.logical_switches
$createls = $segments.Help.create.logical_switch.create()
$createls.admin_state = "UP"

$createls.transport_zone_id = "Enter ID here"
$createls.display_name = "Enter any name here"

$createls.replication_mode = "MTEP"
$segments.create($createls)


To delete logical switch
$logswitchname = Read-Host "Enter the LS name to delete"
#Delete Logical Switch
$logswitchsvc = Get-NsxtService -Name com.vmware.nsx.logical_switches
$logswitches = $logswitchsvc.list().results
$logswitch = $logswitches | Where-Object {$_.display_name -eq $logswitchname}
$logswitchsvc.delete($logswitch.id)


That's it for now but I will keep on adding in the list. In my next post, you will be seeing like connect LS with tier-0 or tier-1 and connect LS with VM with all IP configuration, etc.


Thank you,
vCloudNotes
, ,

NSX-T | Automation Use Case#1

Hello Guys,

Nowadays, I am trying hands and feet over NSX-T automation. It is a bit different than PowerNSX for NSX-V. You can check a few basic instructions and commands on VMware Documentation but here in this post I would like to go a bit deeper and will try to share some Automation Use Cases which you can refer to your daily operations.

Before proceeding further, I would recommend going through the above link and have some understanding of, how you can connect NSX-T manager in PowerShell and how you connect with services of NSX-T.

I hope you have gone through the above link. So, just to recap that, every action in NSX-T which we do through Powershell is executed by recalling a service name. For example,
 

com.vmware.nsx.node
com.vmware.nsx.transport_zones
com.vmware.nsx.logical_switches

If you want to do any specific task on any specific component, then you must know the relevant service for that component. As I said in the above lines, service com.vmware.nsx.logical_switches is responsible for all operations on logical switches. I hope you are understanding it. If not, then feel free to comment and ask your query.

As you know that I always club all these operations into one operation engine which gives me ease of operating it and at a good pace. So, what I have done is, please see in below video.


I will keep on adding many operations in this engine like getting Tier-0 and Tier-1 router detail etc. I mean a lot of options are there to create in.

If you want to have the benefit from it then please continue visiting the space for more engines like this. In case, anyone wants this basic engine then he\she may comment on my blog and then I will share it free of cost :)


Use Case1:

Whenever I create a segment that should be automatically connected with the Tier-1 router.

Solution:

I am working on it guys and will share it once I am done.

Meanwhile, if you want me to add anything here then your all suggestions are welcome.


Thank you,
vCloudNotes 


Thanks for your visit. 
vCloudNotes

NSX-T | Micro-Segmentation

Hello Guys,

Hope you are doing well wherever you are and I pray for everyone's life. Stay Home & Stay Safe!

So, as I promised, I am writing about micro-segmentation means DFW (Distributed FireWall) in NSX-T. This post is for those guys who knows how to configure it in NSX-V. In case, you want to understand DFW in detail then click here.

First of all, let's understand the Connectivity Strategy in NSX-T.

1. Blacklist (with or without logging) - This is the default option which creates an allow all rule in DFW. It also does mean that micro-segmentation is off.
2. Whitelist (with or without logging) - It creates deny all rule in DFW. To allow any traffic, we have to create allow rules. It block DHCP traffic as well if not allowed via allow rule
3. None - This option will disable both Blacklisting and Whitelisting of firewall rules. This option is useful when you have already applied rules from older version of NSX-T

In comparison of NSX-V, above terms were not in picture but default rule was allow-all.

In below video, we are going to explore DFW rules in NSX-T.


Now when we know about the connectivity strategy, let's dig in and know about the DFW rules.

Please go through below video


Feel free to ask any query here.


Thank you,
vCloudNotes


,

NSX-T | Basic Routing Setup

Hi Folks,

As most of the techie guys knows, who are dealing with cloud technologies and specially dealing with VMware cloud applications that NSX-v will sunset soon.

To replace it VMware has already released NSX-T which provides wider support of cloud technologies, easier implementation and independent design approach.

NSX-v was built only for vSphere environment whereas NSX-T can work with any cloud vendor, for example MS Azure, AWS and even with Openstack.

Now a days, integrating k8s with NSX-T is in trend. I will try to create a post on that as well but in today's post let's see how you can setup basic east-west and north-south routing in NSX-T. It will clear many doubts that you might have like what is T0, T1 router? What is SR and DR? and many more.

So, While explaining and demonstrating it, I will be using below topology.

So, let's see how I did it.

Steps are same as in NSX-v, just look and feel is different. Just remember that

Logical switch in NSX-v is similar to Segment in NSX-T
DLR in NSX-v play similar role as Tier-1 in NSX-T (It run on DR that is distributed router)
ESG in NSX-v play similar role as Tier-0 in NSX-T (It has SR that is service router which connect with physical switch\router)

But yes, architecture and configuration is bit different. There was no SR or DR in NSX-v but we have in NSX-T. However this post is to demonstrate the steps to be taken to setup basic routing in NSX-T from my VM to Tier-0 Gateway router.

So what I have already done in my lab :-
  • All VMs are directly connected with Tier-0 gateway through three segments that LS-db, LS-web and LS-app
  • Right now there is no Tier-1 gateway in my lab.

What I will do is:-
  • I will first create one Tier-1 gateway and will connect it to Tier-0 gateway to maintain the topology as shown above
  • Migrate all segments from Tier-0 to Tier-1 and ensure the connectivity
Create Tier-1 Gateway and connect it with Tier-0 Gateway
    Migrate all segments from Tier-0 to Tier-1 Gateway

    Ensure the connectivity now


    So guys, let me know how you found it. I could create one single big video but that becomes bit boring and lengthy.


    Thank you,
    vCloudNotes


    NSX | PacketWalk

    Hi Guys,

    Today I thought to put this kind of packetwalk from my VM in vxlan upto the physical firewall. I checked on internet but couldn't find such exhaustive informatin.

    I hope it will be help for many of you. Please leave your comment as a feedback and let me know how you found it.

    In case of any doubt or you see anything which I should include in below snippet, feel free to say via your comment.


    Thank you,
    Team vCloudnotes
    ,

    NSX-T | Glossary of Components

    I found below useful definition of NSX-T. Thought to share with all.

    Source - VMware Documentation

    Control Plane

    Computes runtime state based on configuration from the management plane. Control plane disseminates topology information reported by the data plane elements and pushes stateless configuration to forwarding engines.

    Data Plane

    Performs stateless forwarding or transformation of packets based on tables populated by the control plane. Data plane reports topology information to the control plane and maintains packet level statistics.

    External Network

    A physical network or VLAN not managed by NSX-T. You can link your logical network or overlay network to an external network through an NSX Edge. For example, a physical network in a customer data center or a VLAN in a physical environment.

    Host Transport Node

    Hypervisor node that has been registered with the NSX-T management plane and has NSX-T modules installed. For a hypervisor host to be part of the NSX-T overlay, it must be added to the NSX-T fabric.

    Edge Transport Node

    Edge node that has been registered with the NSX-T management plane. The Edge Transport Node hosts the NSX Service Routers (SR) that are associated with Tier-0 and Tier-1 routers, including Uplink connectivity to External Networks as well as stateful services such as NAT.

    Profile

    Represents a specific configuration that can be associated with an NSX Edge cluster. For example, the fabric profile might contain the tunneling properties for dead peer detection.

    Gateway Router

    NSX-T routing entity that provides distributed East-West routing. A gateway router also links a Tier-1 router with a Tier-0 router.

    Logical Router Port

    Logical network port which can attach to either a logical switch segment port or a physical network uplink port. Logical Router Ports are also used to connect the LR to SR services such as Network Address Translation (NAT), Load Balancing, Gateway Firewall, VPN etc.

    Segment / Logical Switch

    Segments, called logical switches in previous versions of NSX, are API entities that provide virtual Layer 2 switching for both VM and router interfaces. A segment gives tenant network administrators the logical equivalent of a physical Layer 2 switch, allowing a group of VMs to communicate on a common broadcast domain. A segment is a logical entity that exists independent of the underlying infrastructure and spans many hypervisors. It provides network connectivity to VMs regardless of their physical location, allowing them to migrate between locations without requiring any reconfiguration.
    In a multi-tenant cloud, many segments can exist side-by-side on the same hypervisor hardware, with each Layer 2 segment isolated from the others. Segments can be connected using gateway routers, and gateway routers can provide uplink ports connected to the external physical network.

    Logical Switch Port

    Logical switch attachment point to establish a connection to a virtual machine network interface or a logical router interface. The logical switch port reports applied switching profile, port state, and link status.

    Management Plane

    Provides single API entry point to the system, persists user configuration, handles user queries, and performs operational tasks on all of the management, control and data plane nodes in the system. Management plane is also responsible for querying, modifying and persisting user configuration.

    NSX Controller Cluster

    Deployed as a cluster of highly available virtual appliances that are responsible for the programmatic deployment of virtual networks across the entire NSX-T architecture. NSX Manager and NSX Controller services both exist in the NSX Controller Cluster.

    NSX Edge Cluster

    Collection of NSX Edge node appliances that are logically grouped for high-availability monitoring.

    NSX Edge Node

    Component that provides computational power to deliver IP routing and IP services functions. Service Routers (SR), used for Uplink connectivity and stateful services, are provisioned on Edge node appliances.

    NSX-T Hostswitch or KVM Open vSwitch (OVS)

    Software that runs on the hypervisor and provides physical traffic forwarding. The hostswitch or OVS is invisible to the tenant network administrator and provides the underlying forwarding service that each logical switch relies on. To achieve network virtualization, a network controller must configure the hypervisor hostswitches with network flow tables that form the logical broadcast domains the tenant administrators defined when they created and configured their logical switches.
    Each logical broadcast domain is implemented by tunneling VM-to-VM and VM-to-logical router traffic, using the tunnel encapsulation protocol Geneve. The network controller has a global view of the data center and ensures that the hypervisor hostswitch flow tables are updated as VMs are created, moved or removed.

    NSX Manager

    Management function that exists as a component of the NSX Manager Cluster. In prior versions of NSX, the NSX Manager was a dedicated virtual appliance. As of NSX-T 2.4, the NSX Manager function and Controller Cluster functions are consolidated into a single cluster called the NSX Manager Cluster.

    Open vSwitch (OVS)

    Open source software switch that acts as a hypervisor hostswitch within XenServer, Xen, KVM and other Linux-based hypervisors. NSX Edge switching components are based on OVS.

    Overlay Logical Network

    Logical network implemented using Layer 2-in-Layer 3 tunneling such that the topology seen by VMs is decoupled from that of the physical network.

    Physical Interface (pNIC)

    Network interface on a physical server that a hypervisor is installed on.

    Tier-0 (T0) Logical Router

    Provider gateway router is also known as Tier-0 gateway router, and interfaces with the physical network. Tier-0 gateway router is a top-tier router and can be configured as an active-active or active-standby cluster of service routers. The gateway router runs BGP and peers with physical routers via the service router. In active-standby mode, the gateway router can also provide stateful services.

    Tier-1 (T1) Gateway Router

    Tier-1 gateway router is the second tier router that connects to one Tier-0 gateway router for northbound connectivity, and one or more overlay networks for southbound connectivity. Tier-1 gateway router can also be configured in an active-standby cluster of services when the router is configured to provide stateful services.

    Transport Zone

    Collection of transport nodes that defines the maximum span of logical switches. A transport zone represents a set of similarly provisioned hypervisors, and the logical switches that connect VMs on those hypervisors.

    VM Interface (vNIC)

    Network interface on a virtual machine that provides connectivity between the virtual guest operating system and the standard vSwitch or vSphere Distributed Switch. The vNIC can be attached to a logical port. You can identify a vNIC based on its Unique ID (UUID). The vNIC is equivalent to a network interface card (NIC) on a physical machine.

    TEP

    Tunnel End Point. Tunnel endpoints enable hypervisor hosts to participate in an NSX-T network overlay. The NSX-T overlay deploys a Layer 2 network over an existing physical network fabric by encapsulating frames inside of packets, and transferring the encapsulated packets over the underlying transport network. The underlying transport network can consist of either Layer 2 or Layer 3 networks. The TEP is the connection point at which encapsulation and decapsulation takes place.

    VIrtual Network Interface (VNI)

    The network identifier associated with a given logical switch. As Layer 2 segments are created in NSX, an associated VNI is allocated. This VNI is used in the encapsulated overlay packet, and facilitates Layer 2 separation.


    Thank you,
    vCloudNotes

    , ,

    PowerNSX | Add mulitple static route in NSX Edge

    Good Day Folks,

    During one of the activity, I had a requirement to put multiple (20-25) static routes on NSX edge and doing it one by one and manually is a headache, you know that. right?

    So, I thought to do it through power NSX. Below is the code-

    #Start here

    Connect-NSXServer -NSXserver 192.168.110.42
    $nsxedges = (Get-nsxedge -objectid edge-3).id
    $subnets = '172.16.32.0/24','172.22.12.0/24'      #add all the network which you want to add in static route
    $nexthop = '8.8.8.8'

    Foreach($subnet in $subnets){
    Foreach($nsxedge in $nsxedges){

    Get-NsxEdge -ObjectId $nsxedge | Get-NsxEdgerouting | New-NsxEdgeStaticRoute -vNic 0 -Network $subnet -NextHop $nexthop -MTU 9000 -AdminDistance 1 -Confirm:$false
    }
    }
    #End here

    Refer to below output for an example


    Hope it will help you. Let me know if any doubt or any error.


    Thank you,
    vCloudNotes

    NSX | Working with GRE tunnels

    Hi Folks,

    I found very few article on GRE tunnel creation in NSX so, thought to contribute :) I'll be happy if it is useful for you!

    So, first of all GRE creation is not possible in vCenter NSX GUI. It can only be created via API tool,
    Starting from version 6.4.

    Let's explore how to use NSX API and how to create GRE tunnel.

    Step 1 - Download and install any Rest API client. It can be Postman\Insomnia\Advance Rest Api or any other and open it.

    Step 2 -  Connect NSX Manager in your API client and get edge-id of your target edge (If you don't know already)

    - 2.1 Connect NSX Manager by giving header and authentication information

    Feed header info as shown below-


     And authentication as below-


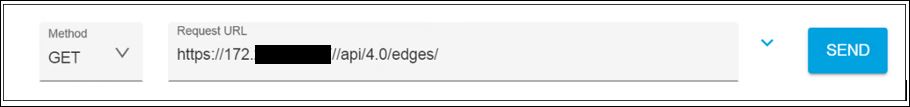
    - 2.2 First, Get your edge-id with below api query if you don't know already. Put NSX manager IP address like, https://NSX_MGR_IP/api/4.0/edges (It will populate all edges in your NSX environment)


    You should get 200 OK response as shown below. Copy the output and paste into some notepad++ kind of app and search the name of your target edge


    Just like below


    Now you know the edge id of target edge. If you know how to, then you can also get it on vCenter GUI as well. right?

    Now, use below text, copy it and modify as per your configuration and paste it in RestAPI "Body" as shown in below image.

    <tunnel>
    <sourceAddress>192.168.200.50</sourceAddress>
    <destinationAddress>192.168.100.11</destinationAddress>
    <name>greTunn</name>
    <description>Gre Tunnel</description>
    <type>GRE</type>
    <enabled>true</enabled>
    <tunnelInterface>
    <mtu>1476</mtu>
    <tunnelAddresses>
    <tunnelAddress>172.20.10.2/30</tunnelAddress>
    </tunnelAddresses>
    </tunnelInterface>
    <greConfig>
    <enableKeepAliveAck>true</enableKeepAliveAck>
    </greConfig>
    <tunnelHealthCheck>
    <enabled>true</enabled>
    <type>PING</type><interval>3</interval>
    <deadTimeMultiplier>3</deadTimeMultiplier>
    </tunnelHealthCheck>
    </tunnel>

    As shown below- Please note the differences and references given in below snippet.


    Now when you will click on Send, it will create a GRE tunnel.

    Note that GRE tunnel doesn't visible in current versions of NSX and might be in future version.

    To test if it is created successfully, there are below ways-

    1. After clicking on Send button in last step, you should have 200 OK reply
    2. Login NSX edge CLI and ping the destination IP address in your tunnel configuration => If pinging then all okay otherwise check the source\destination and tunnel IP address detail.
    3. Again send the GET api call to retrieve vpn tunnels and check if it shows the detail of GRE tunnel.
    4. You can also run a command in ESG CLI "show configuration GRE"

    Now, it was about creation. If you want to delete it then simple, use below api call.

    DELETE https://NSX_IP/api/4.0/edges/{edgeId}/tunnels/{tunnelId}

    It will delete only that tunnel whose tunnel id is given. In above command edgeid and tunnelid needs to be given. If you don't know what is tunnelid, give your comment. I will help you out.


    That's all Guys!!

    Any doubt, feel free to write me up.


    Thank you,
    vCloudNotes


    NSX | Hardware VTEP integration with Arista

    Hi Guys,

    Recently I got opportunity\challenge to configure the hardware VTEP integration with Arista where overlay is NSX.

    After some web-search, I got below URL which explain the exact steps and in very clear and good way. It helped me a lot to configure the CVS on Arista and integrate it on my NSX environment. If you are too looking form similar kind of configuration then it might be useful for you.

    Have a look.

    http://docs.hol.vmware.com/hol-isim/HOL-2017/hol-1703-arista.htm


    Thank you,
    vCloudNotes
    ,

    NSX | BUM Explained

    In network, BUM (Broadcast, Unknown-Unicast and Multicast) is the method of sending and receiving layer 2 network traffic. Let's see what is that-

    Broadcast Traffic - it is used to transmit a message to any reachable destination in the network without the need of knowing the receiver. When Broadcast traffic receives by switch, it send it to all the switch ports except the one it is coming from.

    Unknown Unicast Traffic - It flooded in the network when a switch receives a frame intended for a destination which is not in its forwarding table. In this case, switch mark this frame for flooding and send it to all ports respective of that VLAN. Forwarding this type of traffic can cause unnecessary overload on network and cause poor performance.

    Multicast Traffic - As its name, this traffic allowed a host to communicate with subset of hosts or a group. This caused a broadcast when there is no group mechanism is present in the underlay network or physical network. in NSX, selecting multicast replication mode require IGMP configuration in underlay network and it is totally dependent on physical\underlay network.

    Hope above definitions were helpful for you.


    Thank you,
    Team vCloudNotes

    NSX | How NSX provide more security to datacenters?

    It secure the data center by addressing one of the key issues in traditional security solutions, which are as below-

    1. NSX has visibility not only on virtual datacenter components like VM, ESXi host, portgroups but also within Guest-OS, application and its service hence secure SDDC not only from external attacks but also from within vulnerabilities. Here we know something known as Micro-Segmentation.

    For example:
    if once VM is infected with some viruses\malware or any other malicious software then NSX block the VM and don't allow it to infect other VMs. Below is reference snippet.
    First image(from left) is for traditional datacenter and with traditional security.
    Second image is with NSX


    2. It don't need any in Guest Antivirus agent. Separate antivirus solution is not required if you have Guest-Introspection enabled with NSX. 

    Explanation: I have 10 ESXi host in a cluster and 100 VMs. I'll just prepare my ESXi Host for NSX (Let me know if you want to know about this point) and then enable the Guest-Introspection on entire cluster. My all 100 VMs will be secured with enabled antivirus in Guest-Introspection in NSX.

    3. Because NSX secure entire cluster so if a VM is vMotioned by DRS or restarted by HA on different host then also it will be secured.


    Thank you,
    Team vCloudNotes